Browse by Topic
Popular
Popular Posts
Latest
Latest Posts
Java OutputStream vs Writer: Choosing the Right I/O API
Understand the difference between Java OutputStream and Writer, when to use each, and how character encoding affects text output.
Java InputStream vs Reader: Choosing the Right Stream
Learn the key differences between Java InputStream and Reader: byte-based vs character-based I/O, when to use each, and how character encoding affects your choice.
Java Writer: A Practical Guide to Character Streams
Learn how to use Java's Writer class for character output, including FileWriter, BufferedWriter, and OutputStreamWriter with practical examples.
Java Reader: Reading Character Streams
Understand the Java Reader class, its subclasses, and how to read character streams with proper encoding and buffering.
Java OutputStream: Writing Bytes to Files and Streams
Learn how Java OutputStream works, how to write bytes to files and in-memory buffers, and when to use buffered or unbuffered implementations.
Java InputStream: Reading Bytes and Text Correctly
java inputstream: Learn how to read bytes and text from Java InputStream, handle buffering, avoid common pitfalls, and manage resources safely.
Java IO Basics: Streams, Readers, and File Handling
A practical guide to Java I/O streams: byte vs character streams, readers/writers, buffering, and try-with-resources for reliable file handling.
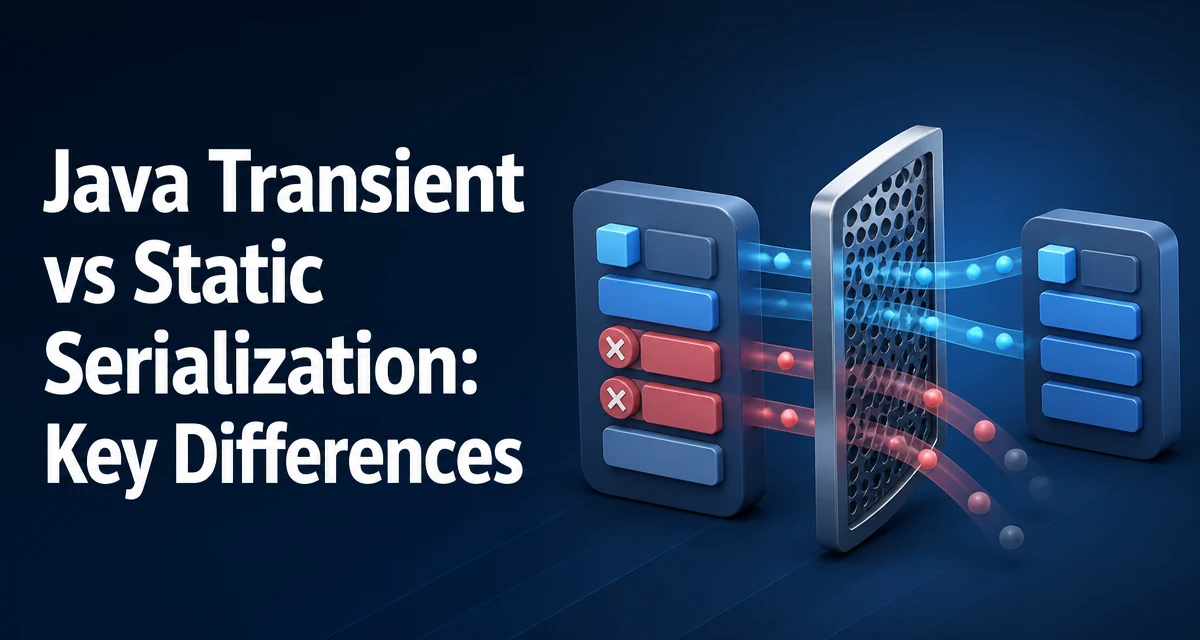
Java Transient vs Static Serialization: Key Differences
java transient vs static serialization: Understand how transient and static fields behave during Java serialization, why they are excluded, and how to handle state cor...
Java Object Deserialization: How It Works and How to Do It Safely
How Java object deserialization works, why deserializing untrusted data is dangerous, and practical protections including serialization filters, validation, and safer formats.
Java Object Serialization: How It Works
Java object serialization converts object state into byte streams. This guide covers Serializable, ObjectInputStream, serialVersionUID, custom serialization, and deserialization security.